Tool Permissions and Least Privilege
Least privilege gives an AI tool only the access needed for its assigned task. Permissions must be enforced by the surrounding system, with clear boundaries between reading, drafting, and acting.
स्रोत
पूरा पाठ सारांश
A teaching assistant can summarize a class document without needing permission to delete it. An agent that drafts a message does not automatically need authority to send it. Least privilege is the security principle of granting only the access necessary for an assigned function. When AI systems use tools, this principle helps limit the consequences of mistakes, ambiguous requests, and malicious instructions embedded in content.
Permissions have several dimensions. A tool may read or modify information, access one course or many, act for one user or an entire institution, and operate for a limited period or indefinitely. A broad credential can quietly erase boundaries that the interface appears to preserve. The surrounding application must authenticate the user and authorize the specific action. A prompt telling the model to behave responsibly is not a substitute for those checks.
Consider a hypothetical assistant that prepares weekly practice summaries. It needs to read approved practice results and create a draft for a teacher. It does not need to change grades, search unrelated student records, or publish the draft. A narrowly scoped service provides only the permitted information and actions. Before any later publication step, the teacher sees the intended audience and content. The authorization applies to that concrete action rather than granting open-ended control over the learning platform.
Tool design can make boundaries easier to enforce. A function that retrieves one authorized document is easier to constrain than a generic command that can access the whole filesystem. Inputs should be validated, and the backend should check permissions again when an action occurs. Temporary credentials, separation of duties, logging, and revocation routes can support the arrangement. Logs should record useful action evidence without becoming a new repository of unnecessary personal information.
OWASP describes excessive agency in terms of excessive functionality, permissions, or autonomy. These distinctions help diagnose a risky workflow. A tool may expose operations the task never needs, hold broader access than the current user, or execute consequential changes without appropriate oversight. Reducing one dimension does not automatically fix the others. A read-only tool can still disclose sensitive information if its data scope is too broad.
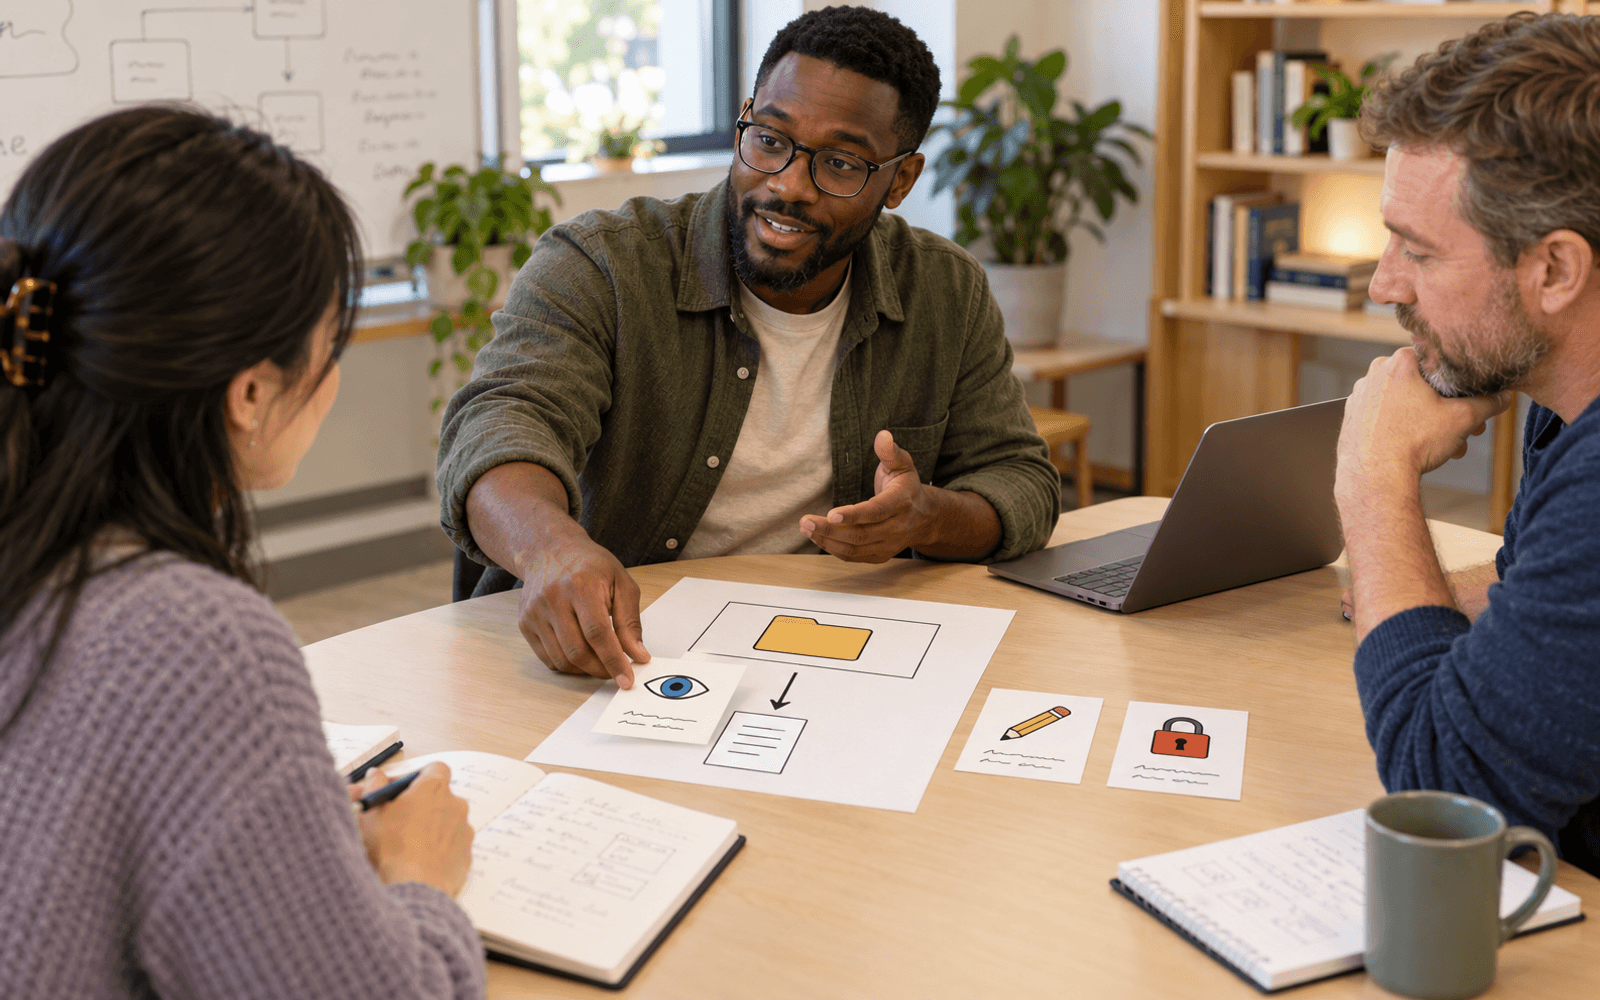
A useful educational exercise gives learners fictional tool cards showing actions, data scope, and expiry. Groups select the minimum set required for a study-planning assistant and explain why each permission is needed. Then introduce a retrieved document that instructs the assistant to send private notes elsewhere. Learners identify which system boundary should block the attempted action even if the model follows the text. Least privilege does not eliminate every AI risk, but it makes the relationship between purpose and authority explicit. Review permissions when tasks change, remove unused capabilities, and test denied actions as deliberately as successful ones.