Product news: Claude Security adds continuous scanning and fix tracking, keeping human review central
Anthropic
AI Product and Learning Report
500-word summary
Listen to the summary
Audio summary
Anthropic announced an updated Claude Security public beta for Claude Enterprise customers on October 21, 2026. The company describes baseline and ongoing repository scans, checks that track whether findings are fixed or recur, and project context that can inform a threat model. API and MCP connections extend access to findings, while role controls govern project activity. These are vendor-described software capabilities. The announcement does not establish that a repository is secure or that using the tool improves students’ programming understanding.
For education teams, continuous review raises an instructional opportunity and a practical evaluation question. A finding can be treated as a claim to investigate, supported by a path through the application and a reason it matters. The following course and pilot examples are editorial proposals. Their value would depend on the task, the review process and the evidence learners can produce, rather than on the presence of an automated security label.
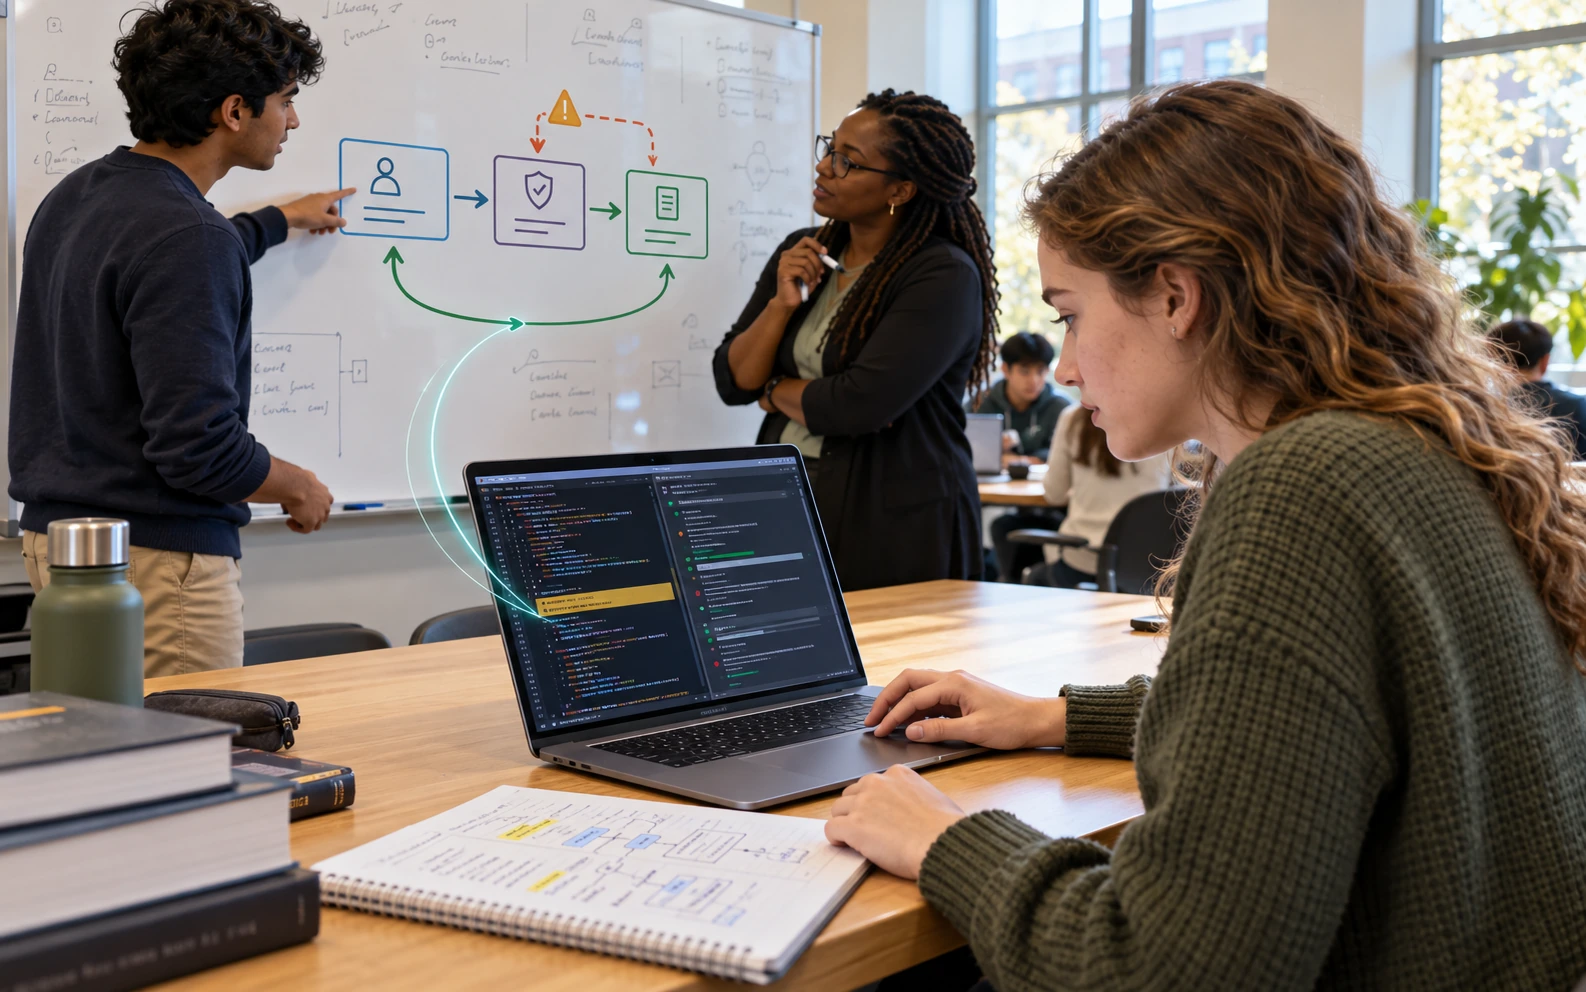
Consider a software engineering class working with a deliberately bounded application containing fictional records. A learner receives a finding about a request that appears to bypass an access check. Before changing anything, the learner would explain the expected permission rule and reproduce the reported behaviour in the course environment. They would then propose a correction and show which case demonstrates that the original defect is addressed. A second case could check that legitimate work remains possible.
The learning task would continue after the first apparent fix. Another student could inspect the explanation, repeat the relevant checks, and identify assumptions that were not tested. If the application later changes, the class could examine whether the finding remains resolved and what evidence supports that judgment. This makes the status of a finding something learners can explain, rather than a badge they simply accept. It also gives disagreement a useful place in the review process.
An institutional pilot could begin with an approved repository and a clearly defined audience for its findings. The team would document the selected branch and scope, the context supplied to the tool, and the reviewer responsible for consequential decisions. It could compare automated findings with its existing review process and examine missed or unsuitable reports. Context added to a project should itself be reviewed, since an inaccurate description of the environment could affect how a finding is interpreted.
Reviewers could retain one rejected finding alongside an accepted correction, with a short explanation of the evidence in each case. This would make the pilot informative even when an automated report is inaccurate, while avoiding an incentive to accept suggestions merely to increase a completion count.
Evaluation should include the effort needed to reproduce findings, assess proposed changes and follow unresolved cases. A course could additionally examine whether learners can explain a similar issue independently after the activity. Those outcomes need direct evidence. The product update offers a more continuous workflow for inspecting software changes, while leaving correctness, security acceptance and educational value as judgments to establish in the setting where the tool is used. For AIEDHK readers, the useful question is how an automated report becomes a reviewable explanation and a justified human decision.